 Ryan Zhang's Blog

Information Leaks — A Responsibility Software Vendors Must Own
Translation Notice
This article was originally written in Chinese and translated into English with the assistance of AI. The translation has been reviewed and edited for clarity, accuracy, and readability. Please refer to the original source where necessary, especially for technical terms, commands, configuration details, and proper nouns.
During penetration tests, I noticed an awkward phenomenon.
Information-disclosure vulnerabilities have become almost routine. These days, an application with no such issues almost feels unusual.
Yet why are problems that should be prevented during development so often discovered only after a system enters production?
At university, we constantly built course projects: one after another, from C to Java and then Python. Eventually I realized that software is largely about creating, reading, updating, and deleting data in databases.
The difference between programmers and ordinary users is simply that one faces a dull SQL console and JSON interfaces, while the other clicks through a polished graphical interface.
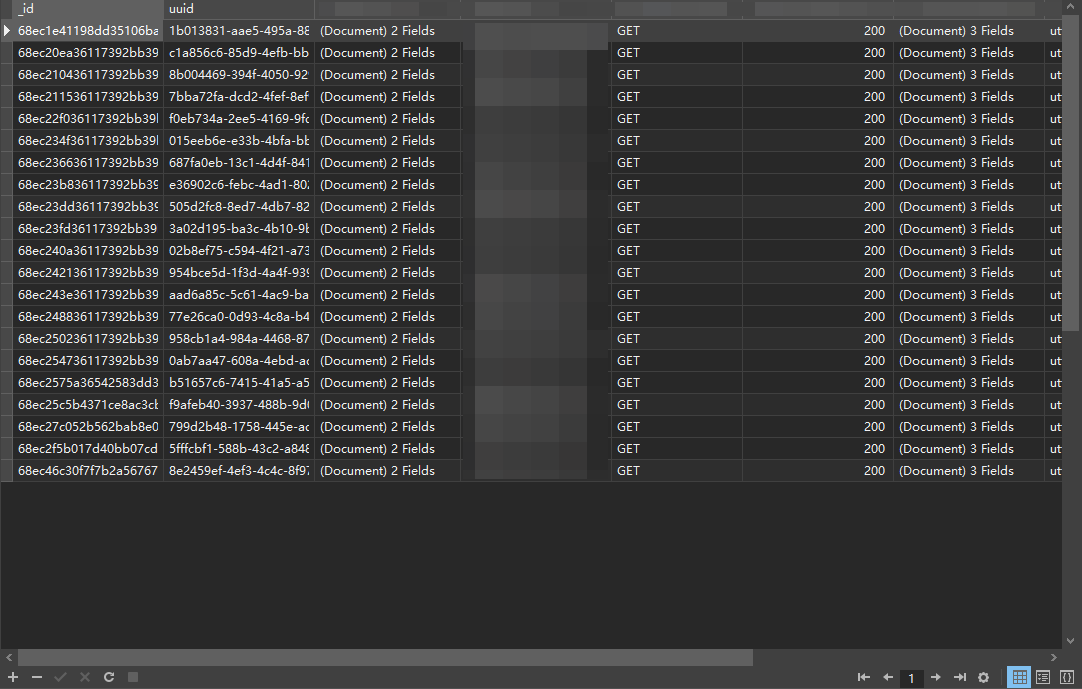
For the aspiring programmers we were at university, sending a password field in plaintext or writing identity-card information directly into a request was hardly unusual.
Security? Hardly anyone mentioned it. The only goal was to make the software run.
Privacy and Convenience: The “Famous Contradiction”
Several years ago, a CEO made a controversial statement:
“Chinese people tend to be more open about privacy. If they can trade privacy for convenience, security, or efficiency, they are often willing to do so.”
There is some truth in this, but also some sadness.
Two or three years ago, while I was still a student, the local police station required students to submit anti-fraud registration information. The provided link led to a site using plain HTTP, without SSL encryption, even though the form requested sensitive information such as identity-card details.
In other words, if I had submitted that data over the campus network, information-center staff could have viewed everything I sent to the police using monitoring equipment.
I acted on impulse and called the local 12345 hotline to complain. A few days later, the police station called back and asked, “How do you think we should fix it? You are the professional in this area.”
That was when I realized that many grassroots organizations do not understand technology. They “complete tasks”; they do not “build systems.”
So the blame for information leaks ultimately falls on programmers.
The Boundary of Privacy Has Long Been Blurred
In today’s Internet, registering an account almost always requires a phone number and real-name verification. Once data leaks, personal information is often exposed together with the number. Doxxing and precise identification through a phone number are no longer unusual.
Many people use secondary numbers to reduce risk, and carriers generally allow up to five SIM cards per person. This helps in theory, but is far from enough. If an application also requires an identity card, you cannot exactly visit the police and apply for “a few more identities.”
Yet legal requirements are precisely what push Internet service providers to collect such information.
China’s Ministry of Industry and Information Technology requires websites providing Internet services within the country to complete registration. The core purpose is to trace responsibility when problems occur. For this reason, sites need real-name systems; from this perspective, software vendors have understandable reasons for requiring identity information. On open forums and communities, inappropriate content may appear at any time, and if the author cannot be identified, the operator is ultimately responsible.
That is also why my own blog does not have a comment section—not because I do not want discussion, but for security and compliance, and to reduce my own risk.
At this point, many people ask:
“Isn’t an IP address the Internet’s identity card? Why do you need personal information if you have an IP?”
That is not wrong, but there are only about 4.2 billion IPv4 addresses, far too few for one-to-one assignment. With widespread NAT, a single IP often represents hundreds or thousands of devices. Finding a specific person from an IP alone is like looking for a needle in a haystack. Real-name information is naturally far more precise.
More realistically, data is wealth.
E-commerce platforms record every click, while short-video platforms record every pause. This behavioral data forms a so-called “user profile”; algorithms use your preferences to recommend content and encourage continued consumption.
The more data, the greater the profit.
Why Do Information Leaks Persist?
In my view, there are two fundamental reasons:
Data Is Wealth: Vendors Want It, but Do Not Protect It
Data supports profiling, analysis, and risk control. Many vendors simply put it into databases in plaintext, without masking or encryption, sometimes even using default passwords. Large companies usually protect their reputations, but can the same be said of smaller vendors? No one can guarantee it.
Developers Often Lack Security Awareness
Many small companies favor recent graduates—they are inexpensive, capable, and compliant. Yet many software-engineering programs have not traditionally taught cybersecurity systematically. Students cut corners at school with a “just make it run” mindset; when that habit enters the workplace, vulnerabilities multiply. Some older programmers who become managers also remain stuck in the mindset of “I wrote it this way before and nothing happened.”
Security proposals from staff are often dismissed with “that is unnecessary,” until something actually goes wrong.
Make the Law the Baseline for Security
The fundamental solution to information leaks is not to rely on penetration testing to patch holes after the fact, but to change things at the source: awareness and responsibility.
If security awareness cannot improve, the law must provide the constraint.
Breaking the law should bring punishment.
One punishment can teach a lasting lesson.
As Luo Xiang once said:
“The law is the baseline of morality.”
Likewise, the law should become the baseline of security.
Closing Thoughts
In recent years, as policies have improved, apps that excessively collect user data and permissions have been removed from app stores. The introduction of unified online identity systems also reflects a maturing policy framework. I hope that one day, companies will be genuinely constrained by law, and information leaks—these “low-severity vulnerabilities”—will disappear from penetration-testing reports.
Support & Share
If this article helped you, please share or support!